

Put your team across the table from a thinking adversary.
Red vs. Blue is a multiplayer cybersecurity strategy game with adaptive adversary AI. Use it to train teams, run tabletop exercises with bite, host tournaments, or finally get non-technical leadership to feel what their SOC is up against.

What it is
The game-based way to learn cybersecurity.
Red vs. Blue combines a real game engine with adaptive adversary AI to make learning cybersecurity actually stick. It works for beginners, experts, and the people who sign the budgets — and it doesn't require any prior technical background, even on the attacker side.
Beneath the game is a full education portal: online courses, labs, scenarios, and a community of operators who've been in the seat for real.
Businesses & organizations
Train staff, run IR tabletop exercises, and prepare leadership for an actual incident — not a slide deck about one.
Educators & training providers
Hands-on game-based learning. Drop it into a curriculum or run a workshop. Students remember it because they did it.
Individual students & professionals
Self-directed practice for cybersecurity learners — from beginners to certified professionals. No command line required.
Event & workshop organizers
Run CTF-style tournaments and live competitions. Spectator-friendly, replayable, and surprisingly entertaining.
How it works
Strategy. Pressure. Receipts.
Pick a side. Pick a scenario.
Choose Red (attacker) or Blue (defender), drop into a pre-built scenario, and you're live in under a minute.
Make moves. Adapt to theirs.
Turn-based strategy with real cyber decisions. Plant a foothold. Detect the foothold. Counter. Recover. Every move has a cost and a consequence.
Debrief. Iterate. Run it again.
Built-in metrics surface what worked, what didn't, and where your team's judgment broke. Re-run the same scenario differently — the AI doesn't play the same game twice.
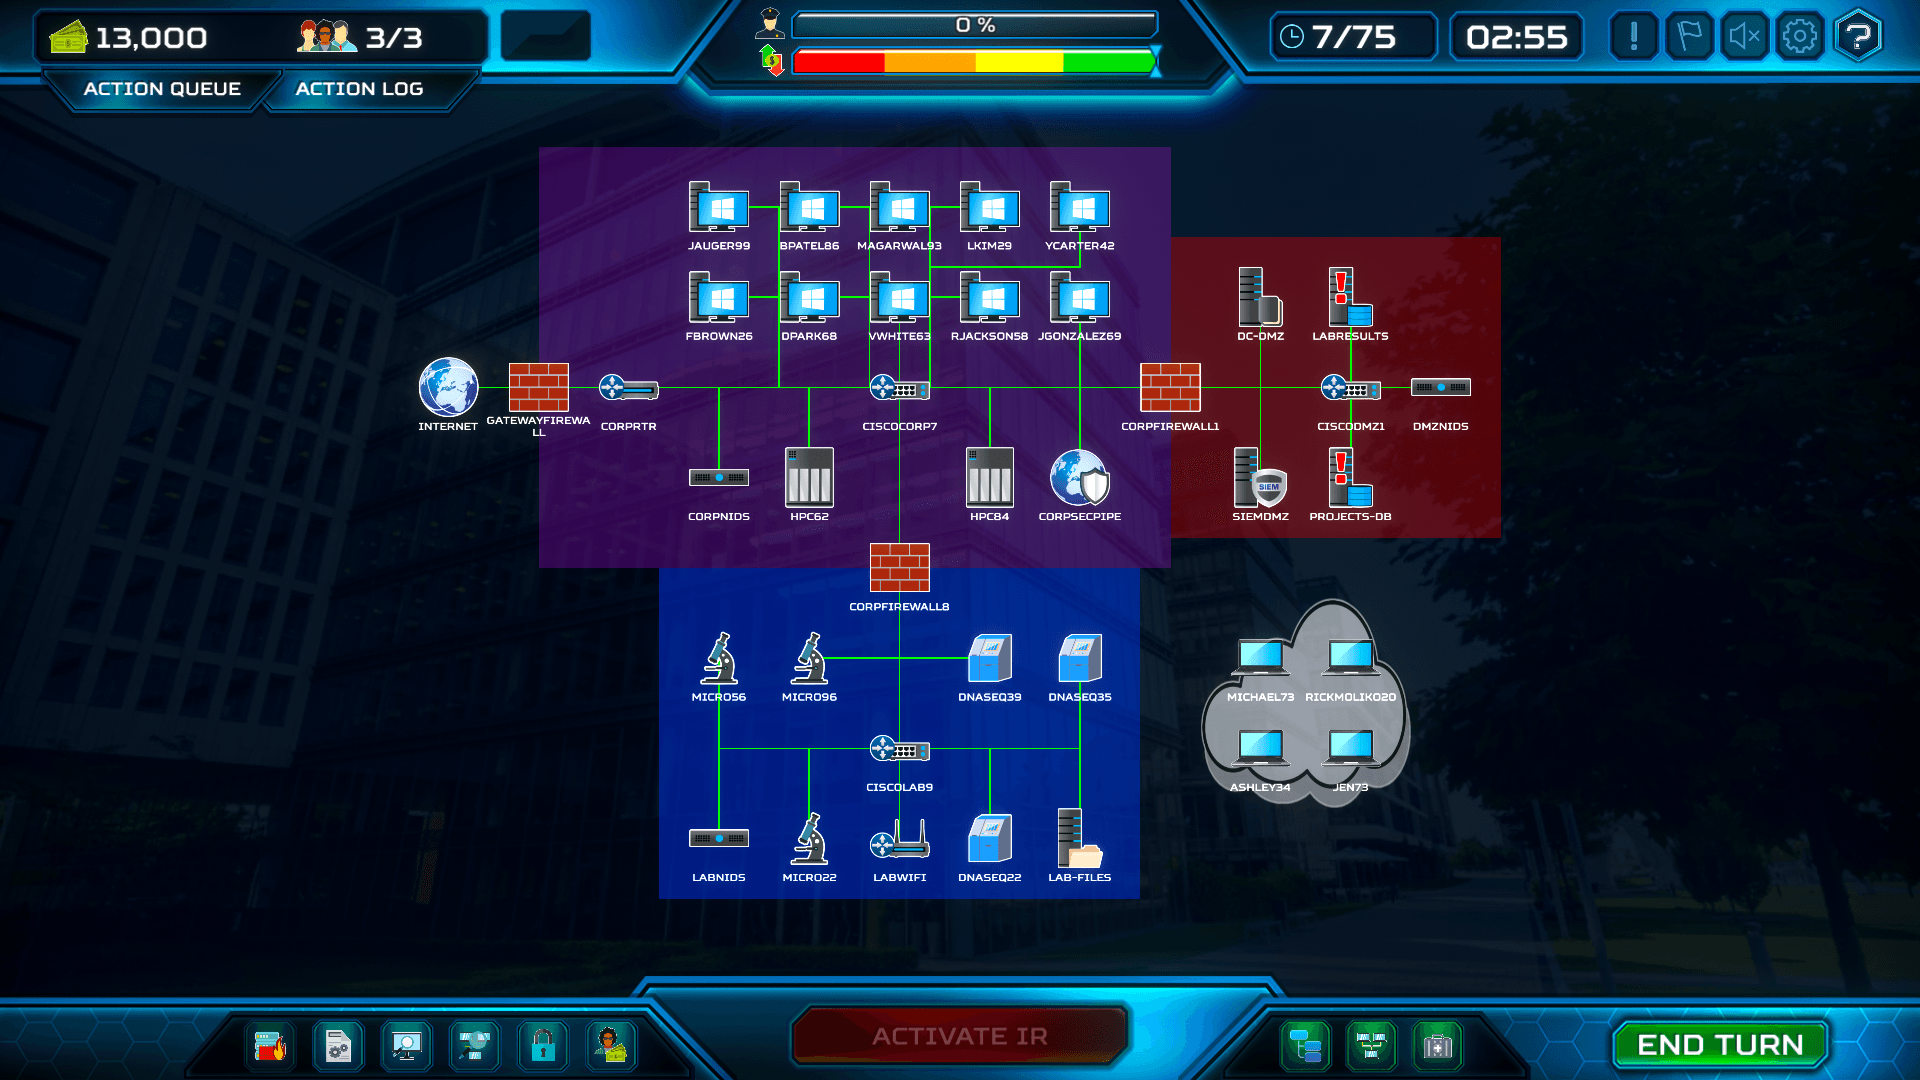
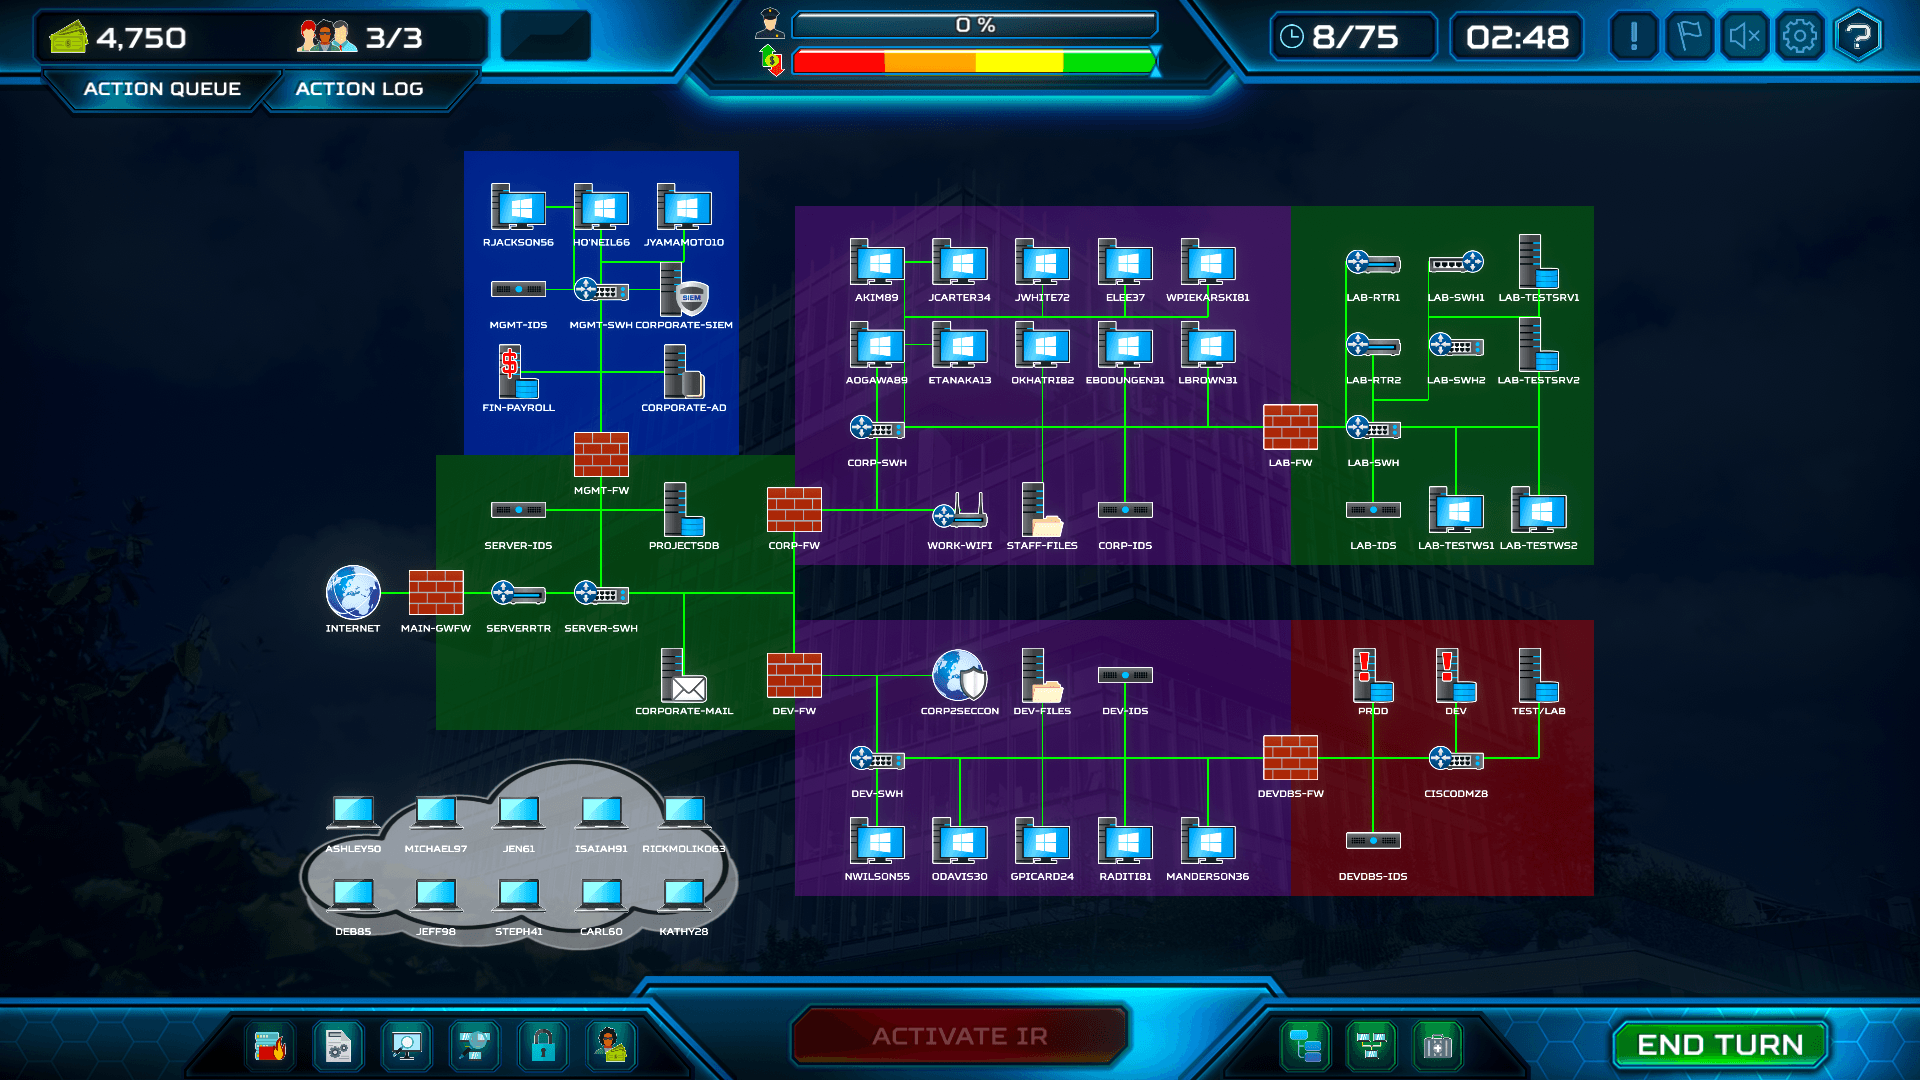
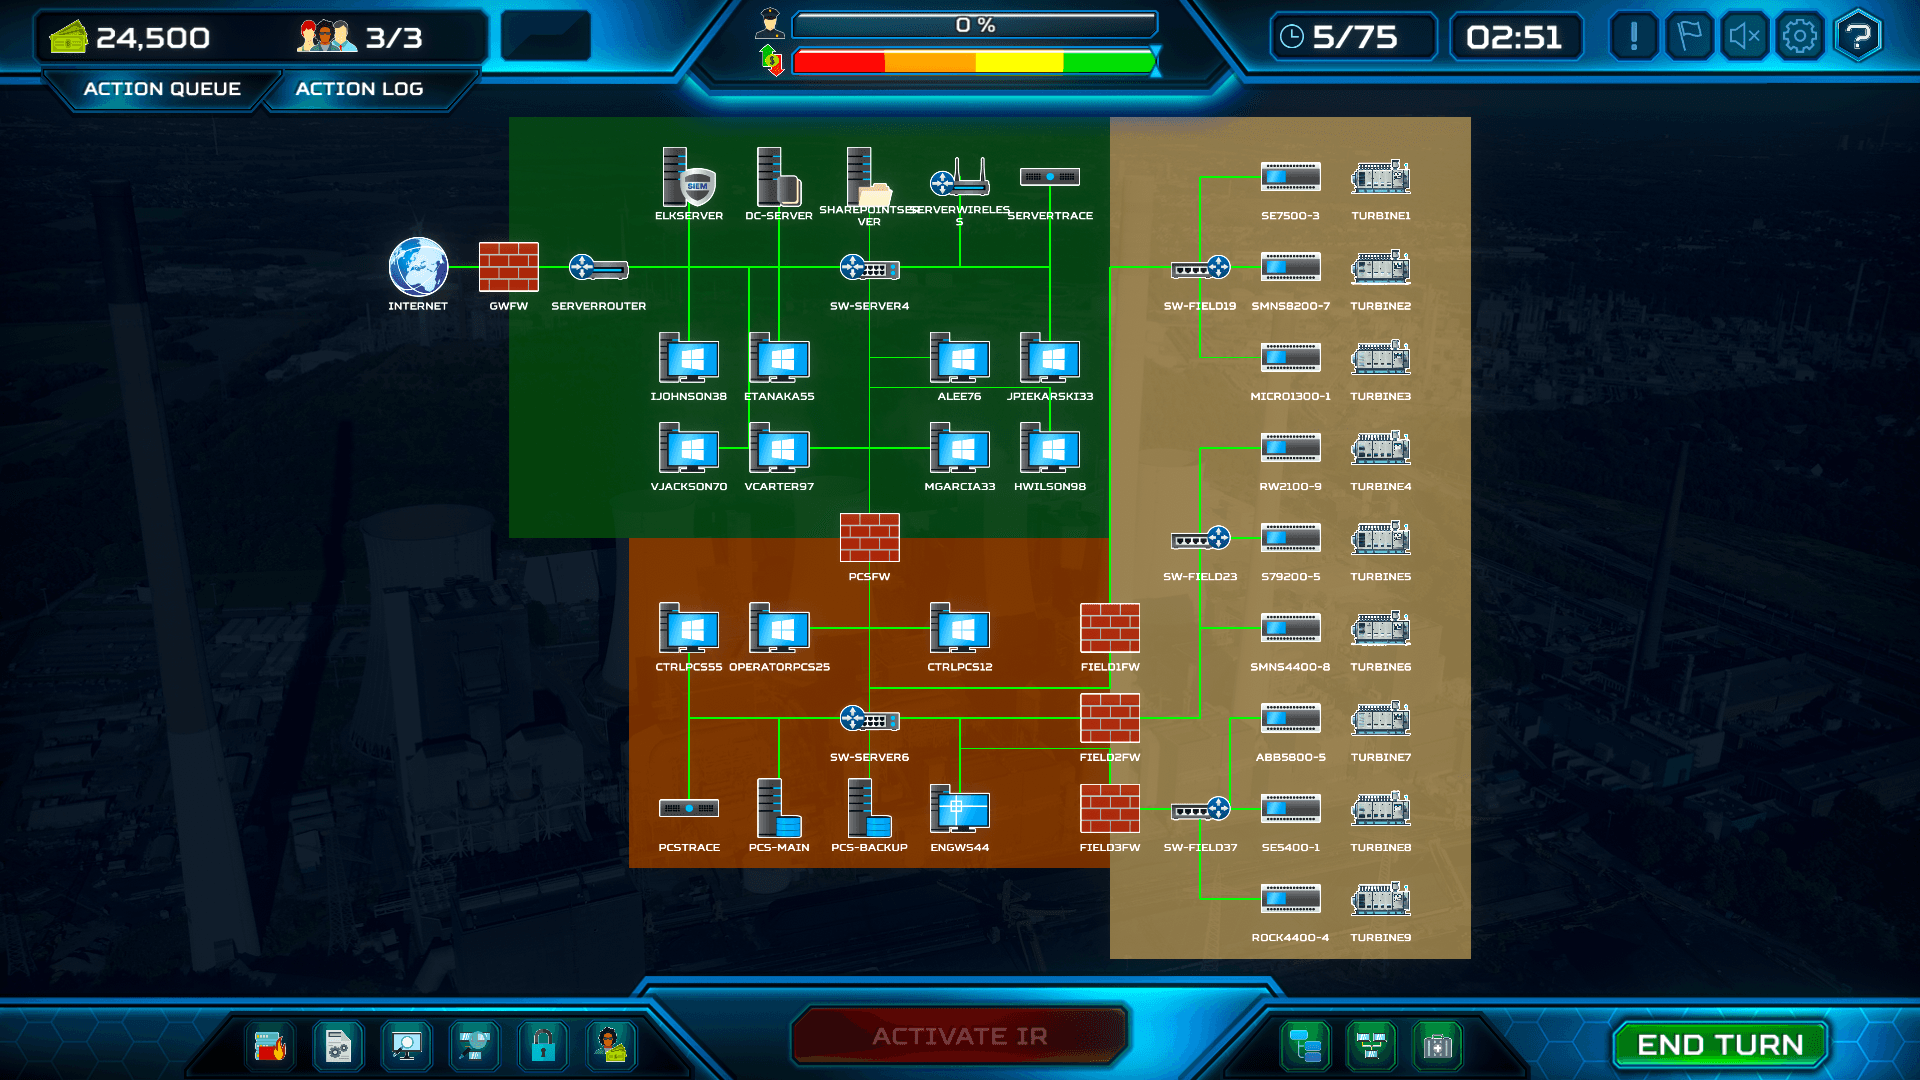
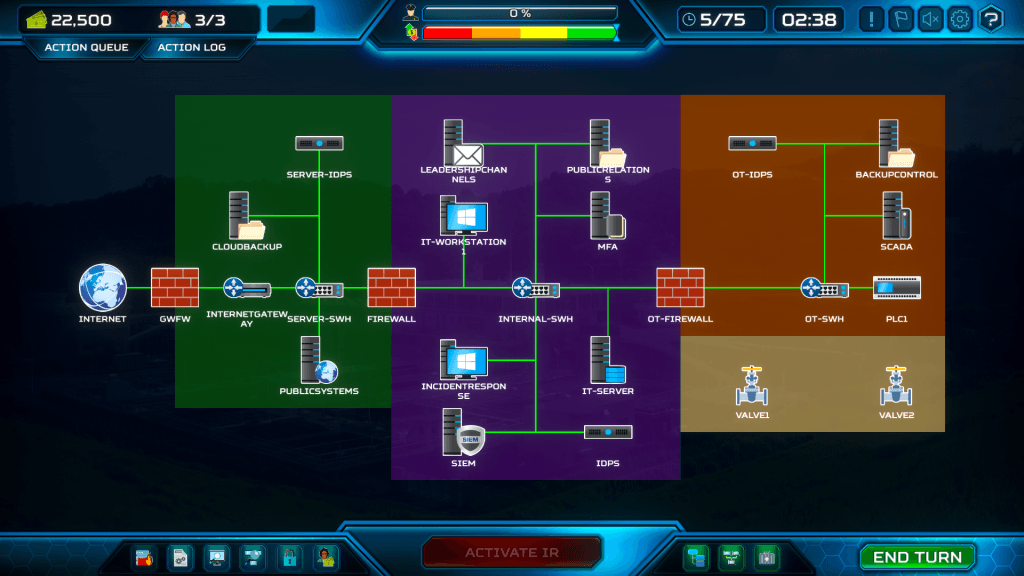
In-game scenario view — multiplayer Red vs. Blue with live AI opponents.
The differentiator
Adaptive Adversary Simulation AI.
Cybersecurity isn't set-it-and-forget-it. Real adversaries probe, pivot, and adjust. The AI in Red vs. Blue does the same — countering your moves, exploiting your blind spots, and refusing to play the same game twice. It's the closest thing to a live op without the legal exposure.
Reads your moves
The AI watches what your team does and adjusts strategy accordingly. Defenders who rely on a single playbook get exposed fast.
Counters in real time
When you change tactics, it changes tactics. New foothold, new evasion, new exfil path — based on what just happened, not a script.
Replays differently
Run the same scenario five times and you'll get five different incidents. Muscle memory builds; complacency doesn't.
What makes it work
Designed by operators. Sharpened by play.
Immersive game-based learning
More than CTF. More than slides. A real game engine, real interaction, real consequences — the format learning research actually backs.
IR tabletop on rails
Tabletop exercises without the spreadsheet. Click-and-run scenarios, immersive environments, and an AI opponent making it feel like an incident.
For leadership too
CISOs, managers, GRC. Strategic and risk-management practice through play — no command line, no certification prerequisite.
ICS / OT integrated
Built with two decades of industrial cybersecurity in the room. ICS / OT environments, content, and scenarios designed by people who've done the actual work.
Performance metrics
Per-player and per-team analytics. Track progress, surface weak areas, and make a real case for your training program's ROI.
Education portal included
Online courses, labs, and an active community. The game is the practice surface; the portal is everything around it.
Built-in scenarios
From pipelines to power plants.
Pick from a library of click-and-run scenarios across IT, ICS, and OT — modeled on real incidents and real operating environments.

Built by people who've done the work
Two decades of ICS / OT security in the design.
ThreatGEN co-founder Clint Bodungen has spent nearly twenty years in industrial cybersecurity and is the lead author of Hacking Exposed: Industrial Control Systems — the standard reference text for ICS security.
That experience is what makes Red vs. Blue's ICS / OT environments feel like the real thing instead of a cybersecurity-flavored arcade game. The scenarios are modeled on actual incidents. The behaviors are modeled on actual adversaries. The control systems are modeled on actual control systems.
Ready to play
Pick a side. Get in the chair.
Sign up for a portal bundle, or book a walkthrough with the team and we'll show you a live game tailored to your environment.